Sales & customer data
Protect the email accounts, workstations, and customer information your sales team uses. Review shared access and account permissions as employees join, change roles, or leave.
Your industry has its own systems, risks, and responsibilities. Explore managed security
From the showroom to the service lane, dealerships run on connected systems — and regulators know it. We keep your DMS available, your customer data locked down, and your store aligned with the FTC Safeguards Rule.
As a dealership handling consumer financial data, these obligations apply to you today — and since 2024, breaches affecting 500+ consumers must be reported to the FTC within 30 days. Here's what the rule demands, and how we cover each item:
Sales, finance, service, and management rely on connected systems throughout the day. We focus on protecting customer information, securing access, and keeping the dealership platforms your staff depend on ready for work.
Protect the email accounts, workstations, and customer information your sales team uses. Review shared access and account permissions as employees join, change roles, or leave.
Support the systems service advisors and managers depend on, including DMS access, connected workstations, and vendor support connections. Prepare recovery procedures for disruptions.
Map where sensitive financing information lives and who can reach it. Separate everyday sales workflows from records that need tighter access.
Make it easy to find sales and service contacts, location details, and inquiry forms on a phone. Review DMS and inventory-feed options before promising an integration.
Explore website design ↗Most dealers that arrange financing or leases must maintain a security program for customer information. The FTC explains the scope and requirements. FTC guidance for automobile dealers ↗
Review one location’s DMS access, business email, endpoints, and recovery plan. Identify security gaps and prioritize the protections your dealership needs.
Dental practices are our original specialty, dating back to 2010. Your practice management system holds valuable patient, insurance, and billing information. A phishing email can give an attacker a foothold long before anyone sees a ransom demand.
A familiar-looking invoice, document link, or support request can catch someone during a busy day. If it leads to stolen credentials or a compromised computer, an attacker may gain remote access and quietly prepare for data theft. The practice may continue working while that access goes unnoticed.
An intrusion may be quiet. Patient-data theft can happen before a visible outage.
A deceptive message leads someone to a false login or malicious content.
Defense: email protection + verificationA compromised account or device can give an attacker access while the office keeps working.
Defense: identity + endpoint monitoringRecords may be copied out of practice systems and used for extortion.
Defense: access limits + investigationIllustrative sequence; attack methods and timing vary. HHS briefing on electronic records and cyber threats ↗
Layer email protection with account safeguards and staff training. Give the team a clear way to verify unexpected payment requests, document links, or remote-support instructions through a known contact.
Synapse Tech manages your technology and security with proven tools, ongoing support, and a team that understands your business.
Review access to practice management systems, imaging, exported files, and backups. Restrict unnecessary permissions and vendor access, and understand which logs and protections your software provider supports.
BUILT AROUND YOUR BUSINESS
Managed IT and security for your dental practice.
Managed endpoint security with SentinelOne and Huntress helps detect and respond to threats.
Strengthen sign-ins with Duo, password management, and Microsoft 365 identity protection.
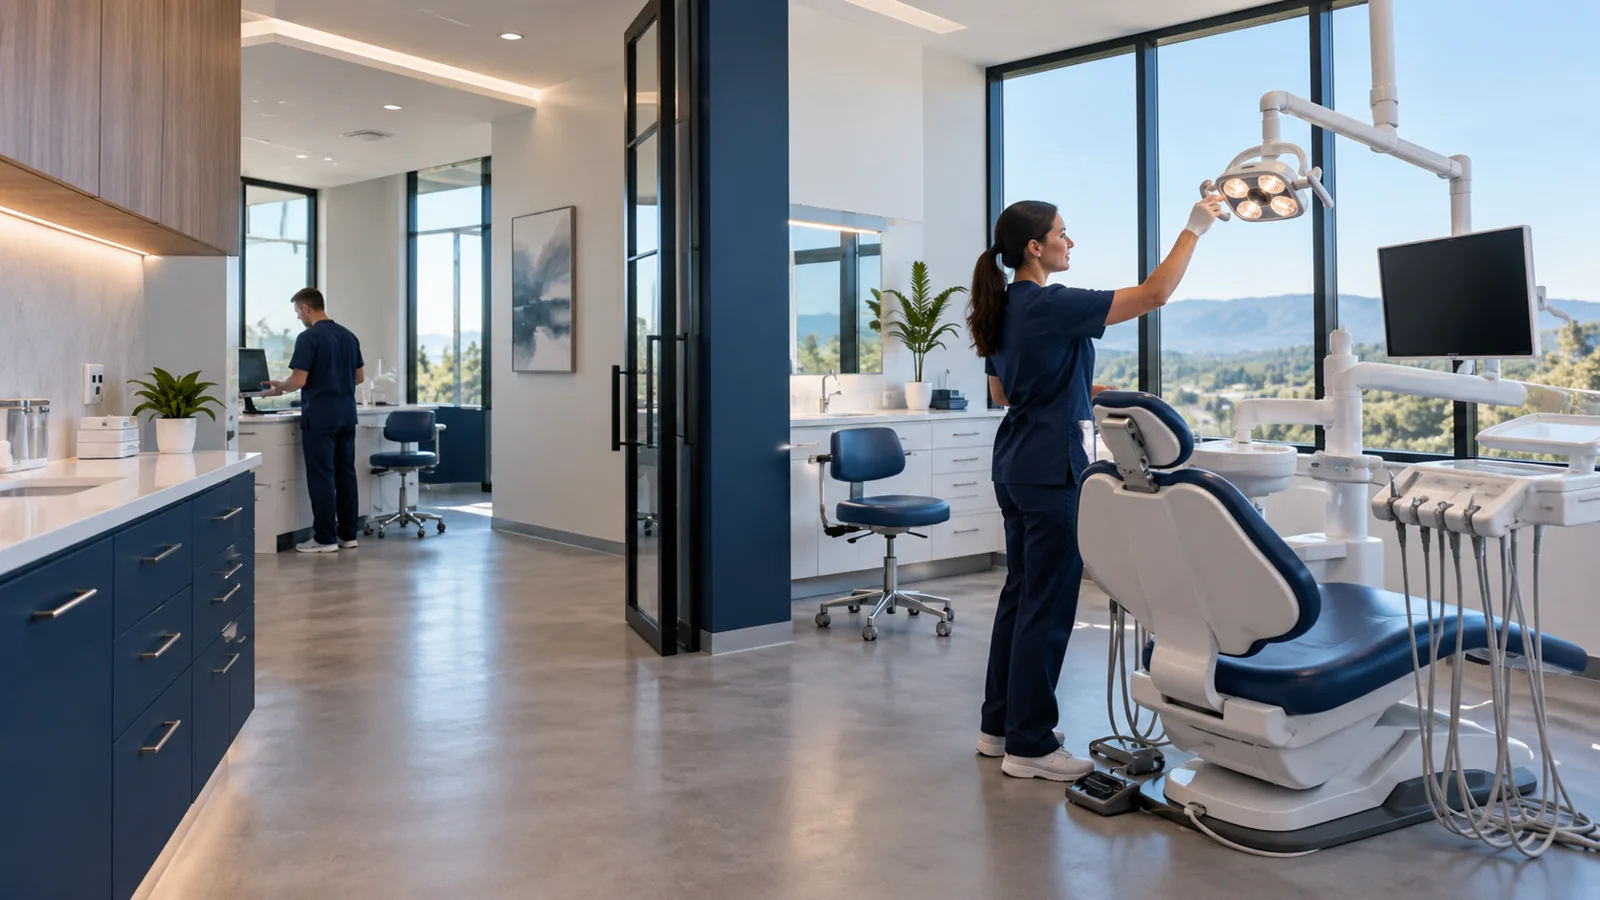
Support workstations, servers, networks, and vendor coordination for practice management and imaging systems.
Patient records. Imaging. Insurance details. Billing information. Protect the systems your team relies on every day.
A backup helps restore information after an outage. It cannot retrieve a copy that has already been stolen. Protecting patient data also means detecting unauthorized access and investigating potential exposure.
Discuss managed IT and data protection ↗Build a process staff can use quickly: report the message, verify unusual requests, and contact the security team if they clicked or entered a password. Fast reporting gives the response team an earlier chance to investigate.
Talk about your practice’s email security ↗We’ll discuss your email provider, practice management software, remote access, and staff accounts to identify where additional protection or monitoring is needed.
It's a set of technical safeguards regulators audit and fine against — and patient data makes dental practices a favorite target, especially on weekends and holidays when no one's watching. Unless someone always is. Here's what the Security Rule demands, and how we cover each item:
From physician-led offices and physical therapy clinics to specialist and other outpatient practices, care depends on trusted information. Your practice software holds patient details, appointments, billing records, and clinical documentation. We protect the accounts, devices, and email around that data and help support your HIPAA responsibilities.
Protect EHR access, referrals, patient communication, and the front-office systems that support MDs and their care teams.
Secure treatment documentation, therapy scheduling, insurance records, and shared devices used throughout the clinic.
Review the software, connected equipment, outside providers, and information handoffs unique to your practice.
A typical practice’s information extends beyond a single application.
Patient records, scheduling, billing, and connected EHR data.
Individual accounts · Access reviewsAuthorized people, workstations, and downloaded information.
Identity controls · Endpoint protectionMessages and attachments sent through approved PHI workflows.
Recipient checks · Protected deliveryA hosted practice system still depends on the accounts, devices, email, and workflows around it. We review those connections with your team and software provider so responsibilities and gaps are clear.
Review individual logins, role-based permissions, multi-factor authentication options, vendor access, and staff departures. Assess record exports, local storage, audit capabilities, and recovery arrangements around your actual software.
Configure hosting, account protection, and encrypted message delivery around your PHI workflows. Review provider agreements, recipient access, forwarding rules, and staff instructions before treating email as an approved channel for patient information.
Connect technical controls to documented responsibilities: risk analysis, access reviews, staff training, incident handling, backup recovery, and vendor oversight. Keep evidence of what is configured and how it is maintained.
HHS permits email transmission of electronic PHI when it is adequately protected. The appropriate safeguards depend on the practice’s risk assessment and communication circumstances. HHS guidance on email transmission ↗
Email hosting alone does not establish HIPAA compliance. The practice also needs appropriate policies, configuration, workforce procedures, and business associate agreements where required. We help connect the technology with those responsibilities.
HHS guidance on cloud providers and BAAs ↗The HIPAA Security Rule addresses administrative, physical, and technical safeguards for electronic PHI. Risk analysis, access controls, activity review, and contingency planning belong in the overall program. HHS overview of the HIPAA Security Rule ↗
Tell us what kind of care you provide and which practice management software and email provider you use. We’ll discuss where PHI is stored and sent, who can access it, and which protections need attention.
Agents, brokerages, and property teams balance inquiries, documents, and follow-ups throughout the day. We help protect sensitive client information, secure business email, and build a website that reflects your business.
Agents, coordinators, and property teams move between conversations, documents, and deadlines. We focus on protecting the accounts, devices, and documents that keep those transactions moving.
Showcase your people, service areas, and expertise with a clear path to contact the right agent. Assess listing-feed permissions and platform options before adding property integrations.
Explore website design ↗Real estate wire fraud can involve impersonated parties and altered payment instructions. NAR provides guidance for recognizing the risk and independently verifying instructions. NAR guide to real estate wire fraud ↗
Start with a review of business email, device protection, and access to client documents. Keep payment approvals under direct human control.
A school day connects students, teachers, administrators, and families. Behind it are student records, staff email, classroom devices, and office systems. We help protect those connections so your team can focus on education.
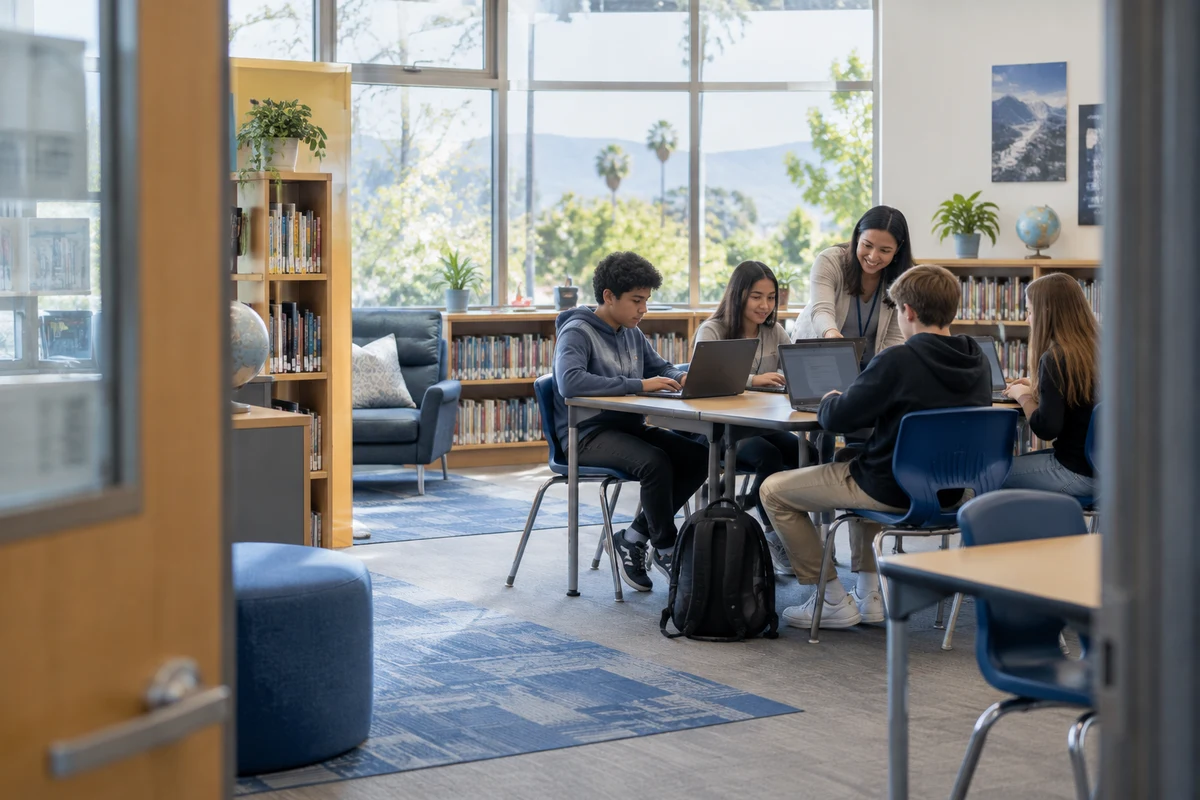
A student device should not have the same access as a payroll workstation. We help map the people, systems, and networks on your campus, then organize protection around how each is used.
Review access to enrollment, attendance, learning platforms, personnel files, and school office records. Limit permissions by role and update accounts as students enroll, staff change positions, or people leave.
Inventory classroom computers, staff laptops, shared devices, and network equipment. Separate student, staff, administrative, and guest access; manage updates and protection for the devices the school owns.
Protect staff accounts with appropriate sign-in controls and email defenses. Build a simple reporting process for fake administrator requests, unexpected login prompts, suspicious attachments, and changes to vendor payment details.
Synapse Tech manages your technology and security with proven tools, ongoing support, and a team that understands your business.
Build a clear, mobile-friendly school website for admissions, calendars, announcements, and staff contacts. Keep public information separate from student records, with clear links to the school’s approved portals.
Explore AI website design ↗Tell us about your devices, learning and office platforms, network setup, and existing IT support. We’ll identify the security and continuity priorities that fit your school.
Accounting firms, law offices, consultants, and other professional teams work with information clients cannot afford to expose. We help protect business email, confidential files, and the devices your people use in the office and on the move.
Tax documents, legal matters, project files, and private business plans pass between people, applications, and locations. We focus on controlling those handoffs without making everyday work harder.
Review shared folders, document platforms, client portals, and external sharing links. Organize access around clients, matters, and projects, with a clear process for ending access when an engagement or staff role changes.
Help defend against fake partner requests, altered invoices, stolen account sessions, and malicious attachments. Review sign-in protection, forwarding rules, and a separate verification process for sensitive instructions.
Manage supported laptops and workstations, software updates, endpoint protection, and remote access. Plan for lost devices, staff departures, and recovery of the documents your team needs to meet deadlines.
Synapse Tech manages your technology and security with proven tools, ongoing support, and a team that understands your business.
Present your services, team, and specialties clearly. Give prospective clients a simple way to make contact, and direct sensitive documents to your approved secure portal instead of a public inquiry form.
Explore AI website design ↗Tell us about your client files, business software, email, and remote team. We’ll review where access, device protection, and recovery need attention.
Call us or request your free security risk assessment.
Get My Free Risk Assessment 888-669-1988